Security of the software delivery process

Cybersecurity for technology companies
and financial services

We address the technical requirements of
NIS2 UKSC DORA CRA ISO/IEC 27001 SOC 2

CRA Platform

For manufacturers, importers and distributors of products with digital elements — compliance evidence kept separately for every version you ship.

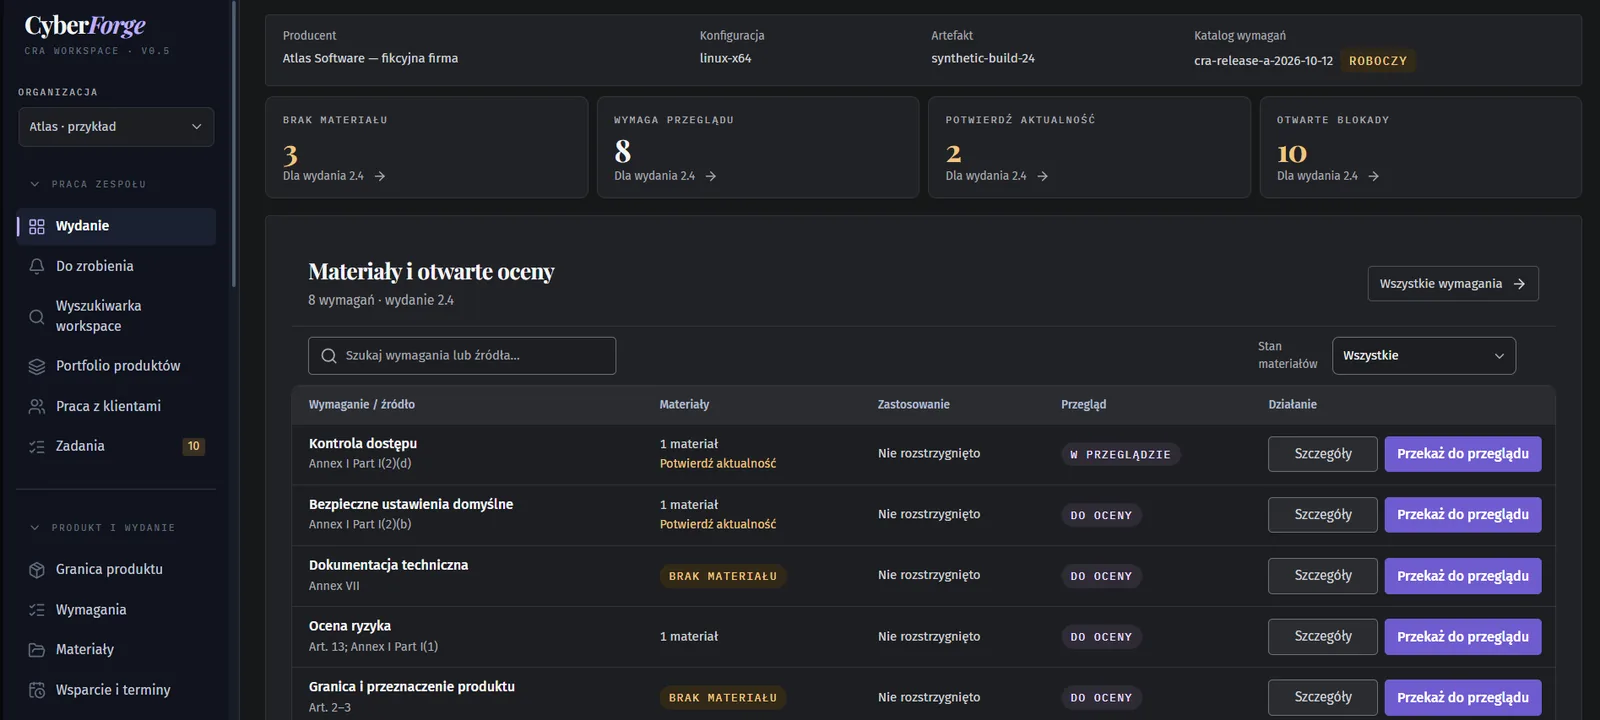
CRA Platform — product releases with their materials, gaps and decisions

The documents the CRA requires come out of your team's everyday work — no rush to assemble them the week before an audit

Lower risk of a fine for a late report: the platform counts the time from the moment you learn about an issue and shows who is responsible

When a new security flaw is published, you see straight away which versions of your product it affects and what you did about it

Your auditor gets one evidence package they can check themselves — instead of weeks of sending files and explanations

How we work

What changes in your company

You ship faster

Security stops being a gate you have to clear right before release. Controls run in the background, on every code change, without meetings or waiting for someone's sign-off.

Audits stop halting the work

A failed audit is not a bad grade on paper. It is a blocked deployment, a frozen contract, and a team that spends weeks collecting evidence in reverse instead of shipping. When evidence is produced automatically, the audit comes down to showing evidence you already have — not a company-wide standstill.

Costly surprises disappear

A vulnerability surfaces at code review, not in a customer report or a pentest two weeks before signing. At that point the fix costs a fraction of what it would later.

Technology companies
and financial services

Banks, fintechs, SaaS companies, software houses and software vendors covered by NIS2, the Polish KSC Act, DORA and the CRA — and their suppliers. We handle the technical part of the requirements. You handle the organisational and legal part with your adviser.

The auditor asks who approved the change

The questions go deeper: how the code is produced, who approves it and what reaches production. We prepare evidence an auditor can check.

  • ICT systems and suppliers
  • Evidence that controls work
  • Board accountability

You grow faster than your process keeps up

You ship every day, yet your requirements match a bank's. We set up controls so speed and compliance go together.

  • Frequent releases
  • Supplier risk
  • Business continuity

Security is blocking your sales

A client sent a security questionnaire or requires a certificate, and the contract is on hold. We close the gaps and prepare answers backed by evidence.

  • A questionnaire before signing
  • SOC 2 or ISO 27001
  • Clients in the US, UK and DACH

Your product falls under new regulations

Since 11 September 2026 an actively exploited vulnerability in a digital product must be reported within 24 hours, including in versions already sold. Technical documentation comes on top.

  • Vulnerability reporting
  • Documentation and supply chain
  • Customer requirements

Fill in the form

We'll get back to you within 24 hours on business days. The call is free.

The data you send goes to CyberForge sp. z o.o. and is used to reply to your enquiry.Privacy policy